Compliance Core
$99/mo
or $990/yr, billed annually
Getting SOC 2 evidence under control
AWS + GitHub · AuditFetch Local
Collect evidence with read-only connections. Review it against your requirements. Keep evidence and source credentials in your own environment.
SOC 2 evidence software from $99/mo per organization.
Published pricing in USD. Unlimited team members. No per-seat fees.
Software subscription. Your infrastructure and audit fees are separate.
We deliver the signed package and evaluation license before you install. On a phone? Request delivery now and install later on a suitable host. Inspect a sample packet.
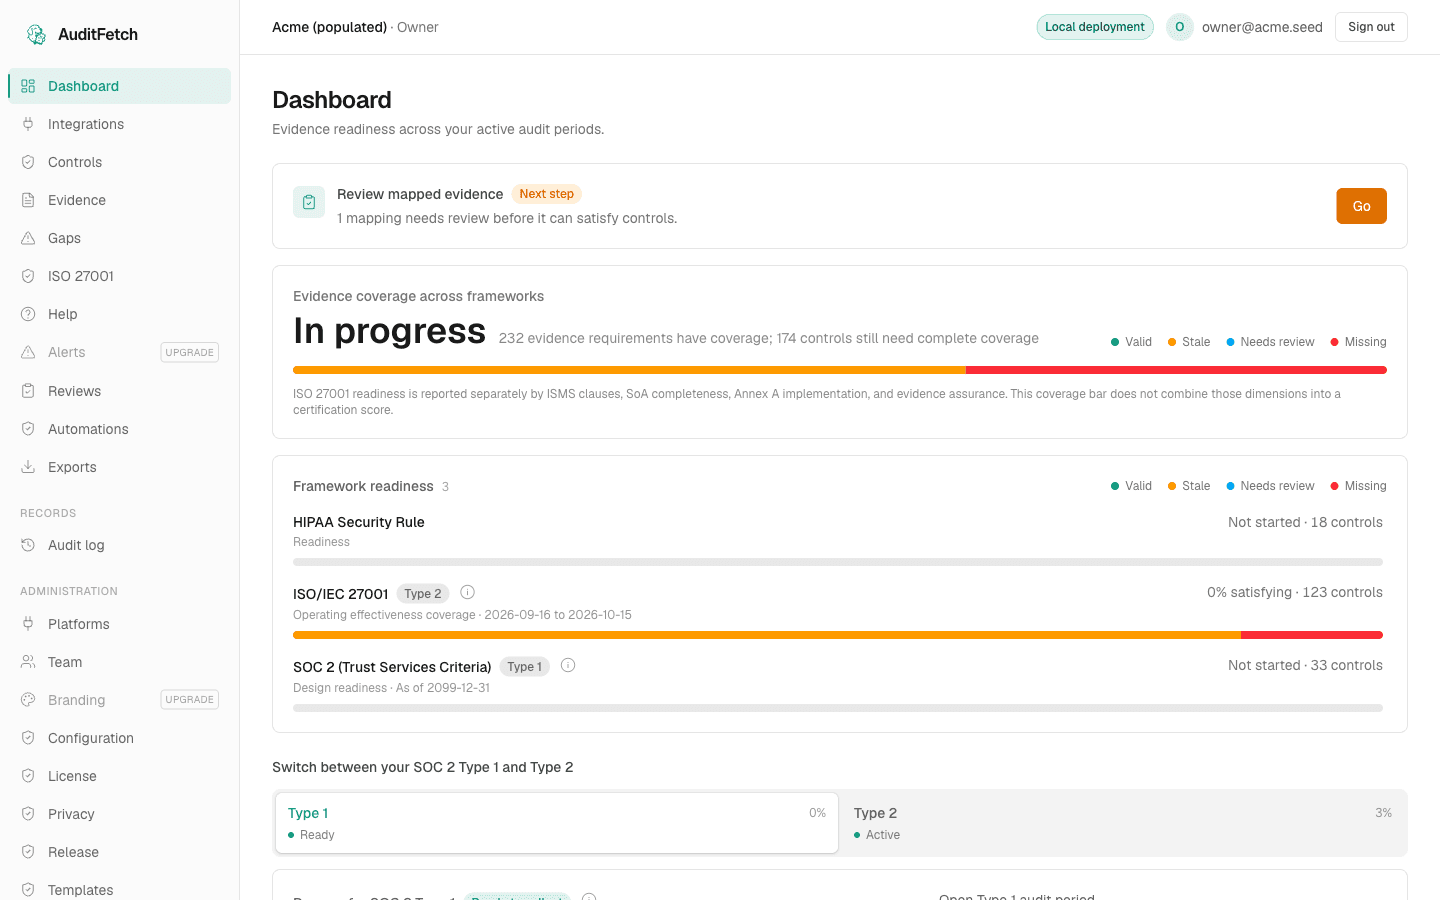
Start with one AWS or GitHub source. Confirm one useful artifact before you expand collection.
Step 1
Select the AWS account or GitHub organization and repositories you control. Configure read-only access and verify the connection.
Step 2
Run collection and inspect an artifact. Check its source, capture time, content hash, and validation result.
Step 3
Open the mapped requirement. Review whether the artifact supports it and check whether the evidence is current.
Step 4
Select the audit period and reviewed evidence. Export a PDF, ZIP, or CSV packet for your auditor.
Use recurring collection to keep evidence current. Capture time and freshness help your reviewers identify evidence that needs attention. A content hash helps detect a changed artifact; it does not prove that a control is effective.
Evidence, source credentials, and audit history stay in your Local deployment. Licensing and update checks exchange their documented metadata. Optional Local telemetry is off by default.
If you enable an external AI provider, review its data handling before use. Local model options are also available.
Review security and data handling$99/mo
or $990/yr, billed annually
Getting SOC 2 evidence under control
$149/mo
or $1,490/yr, billed annually
Running SOC 2 and HIPAA together
$299/mo
or $2,990/yr, billed annually
Preparing for ISO 27001 certification
Prices are per organization in USD. Software subscription. Your infrastructure, audit fees, and optional external services are separate. AuditFetch supports readiness and evidence review. It does not issue certifications or guarantee an audit result.
Yes. Use AuditFetch to collect, review, and export evidence for your process. Confirm your auditor’s format and scope requirements before the evaluation.
We confirm delivery and your setup window before license issuance. Setup time depends on your host and access approvals. The standard evaluation lasts 14 days from issuance, with no grace period or automatic paid conversion.
No. Reviewers must assess evidence and control effectiveness. AuditFetch supports that review; your auditor makes the audit decision.
Check the capability list for supported sources and limits. Browser, Vanta, and Drata remain in Preview and are outside this AWS/GitHub evaluation path.